Manufacturing. IT and OT visibility.
Security starts with understanding the process.
Connect the network picture with production realities.
In a manufacturing facility, IT assets coexist with PLCs, HMIs, SCADA, engineering workstations and IoT devices. Some systems operate for many years, have limited update options or require vendor approval for changes. Standard inventory and vulnerability practices must be adapted to those conditions.
Armis Centrix for OT/IoT Security helps build a picture of devices and communications and analyse weaknesses in operational context. These data can support joint work by IT, OT and security to protect production processes.
From information
to action.
Understand the devices
Enrich the inventory with industrial devices, available technical characteristics and relationships with IT infrastructure.
Observe connections
See communications between zones and compare them with the intended segmentation model.
Adapt the response
Assess vulnerabilities with process criticality, legacy systems and available maintenance windows in mind.
How to start?
- Start jointly with IT and OT: identify a line or segment, owners, critical devices and observation constraints.
- Agree on data collection architecture and deployment options. For isolated environments, review the On-Prem requirements.
- Evaluate identification quality and event usefulness, then validate proposed changes with the production process owner.
Requirements and limitations
Monitoring does not guarantee production continuity or that every integration has no environmental impact. Data collection methods, including selective queries, must be approved for specific devices. Asset information can support work with IEC 62443 or NIST, but does not constitute certification or proof of compliance.
Illustrative use case
Two networks.
A shared view.
The plant environment
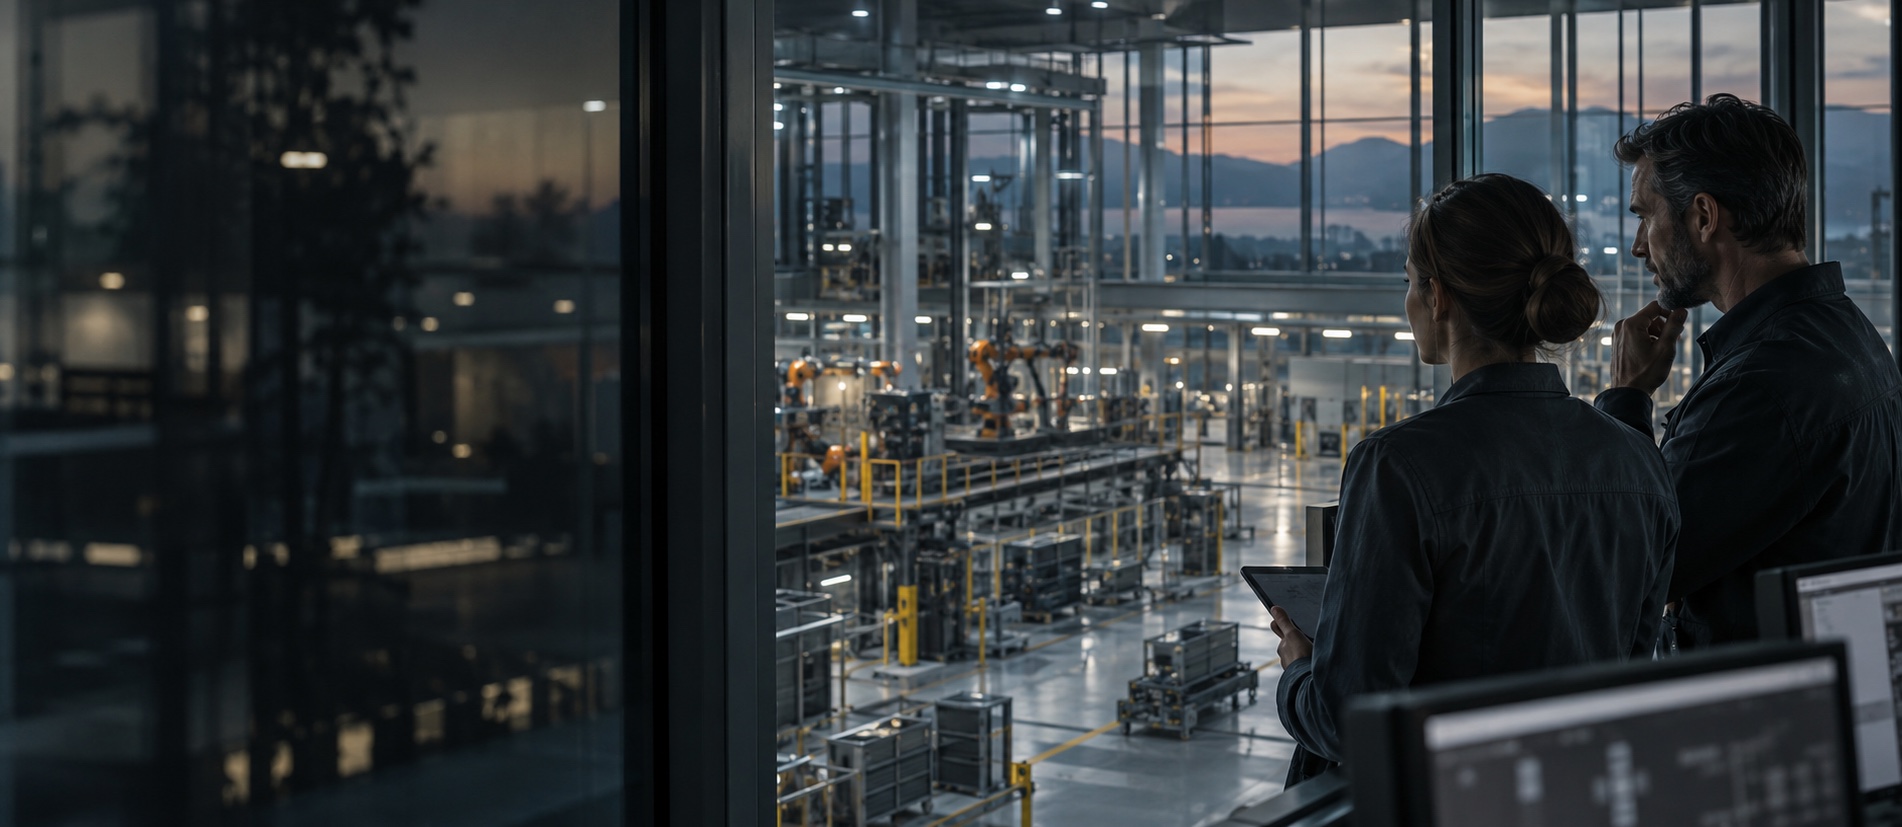
A plant wants to review communications between office and production networks. The IT/OT team jointly defines the scope of observation and further investigation.
A shared IT/OT review plan
Observation scope
Choose the segment and communication observation points.
Device profiles
Validate which devices operate within the selected area.
Cross-zone connections
Review connections to plan further checks and changes.
Related topics.
Your questions.
Clear answers.
Can devices that cannot be scanned still be observed?
Analysis of mirrored traffic can provide data without running a scanner against a device. Visibility depends on protocols and observation points. Additional queries require separate agreement.
What about legacy systems?
First establish their profiles, communications and process importance. If updates are not possible, IT/OT owners assess exposure reduction and compensating controls.
Does Armis implement network segmentation?
Communication visibility and asset context can support segmentation design and validation. Rule enforcement depends on network infrastructure, integrations and an approved change process.
How should an initial evaluation scope be prepared?
Choose a representative segment, define permitted collection methods and agree measurable criteria, such as identification accuracy and visibility of specified connections. Do not assume a fixed evaluation duration or outcome.
Let’s talk about
your environment.
From where you are to what comes next.